In December 2021, log4j vulnerability gave unauthorized users access to confidential IT resources. How prepared was your organization to mitigate and remediate the risk? Security threats like this require a new approach of security by design.
In today’s DevOps Huddle, we’ll discuss:
Software supply chain risks
Shift left pipeline to integrate security into design
How a F100 conglomerate fixed log4j issues in 24 hours using Opsera
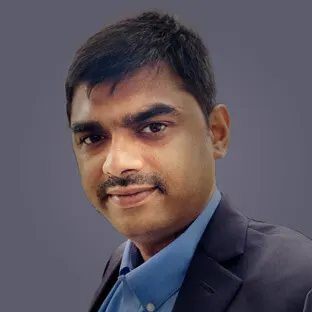 Vishnu VasudevanCPO, Opsera
 Rajeswar Rajendran
 Srinath Vasudevan