Closing the Security Gap in AI Modernization
AI makes modernization much faster, but if you rewrite code without seeing what's in it, hidden vulnerabilities and compliance gaps move straight into your new environment. The latest Forge release adds discovery, security, and governance features so every stakeholder shares one view of a legacy system before any new code ships.
New governance and compliance features in Opsera Forge
Every enterprise runs legacy apps nobody fully understands. The original builders are gone, the documentation is missing, and teams are afraid to touch the code. AI makes modernization much faster. But if you rewrite code without seeing what's in it, hidden vulnerabilities and compliance gaps move straight into your new environment.
The latest Forge release adds discovery, security, and governance features. Product, security, and engineering leaders now share one view of a legacy system before any new code ships.
Application Portfolio Intelligence
Point Forge at a repository and it builds a technical spec and a business profile. Business rules, data flows, and dependencies are mapped directly from the code, and a guided wizard fills in missing context. The profile updates automatically when the code changes. You can also connect several repositories to one application and view it as a single system.
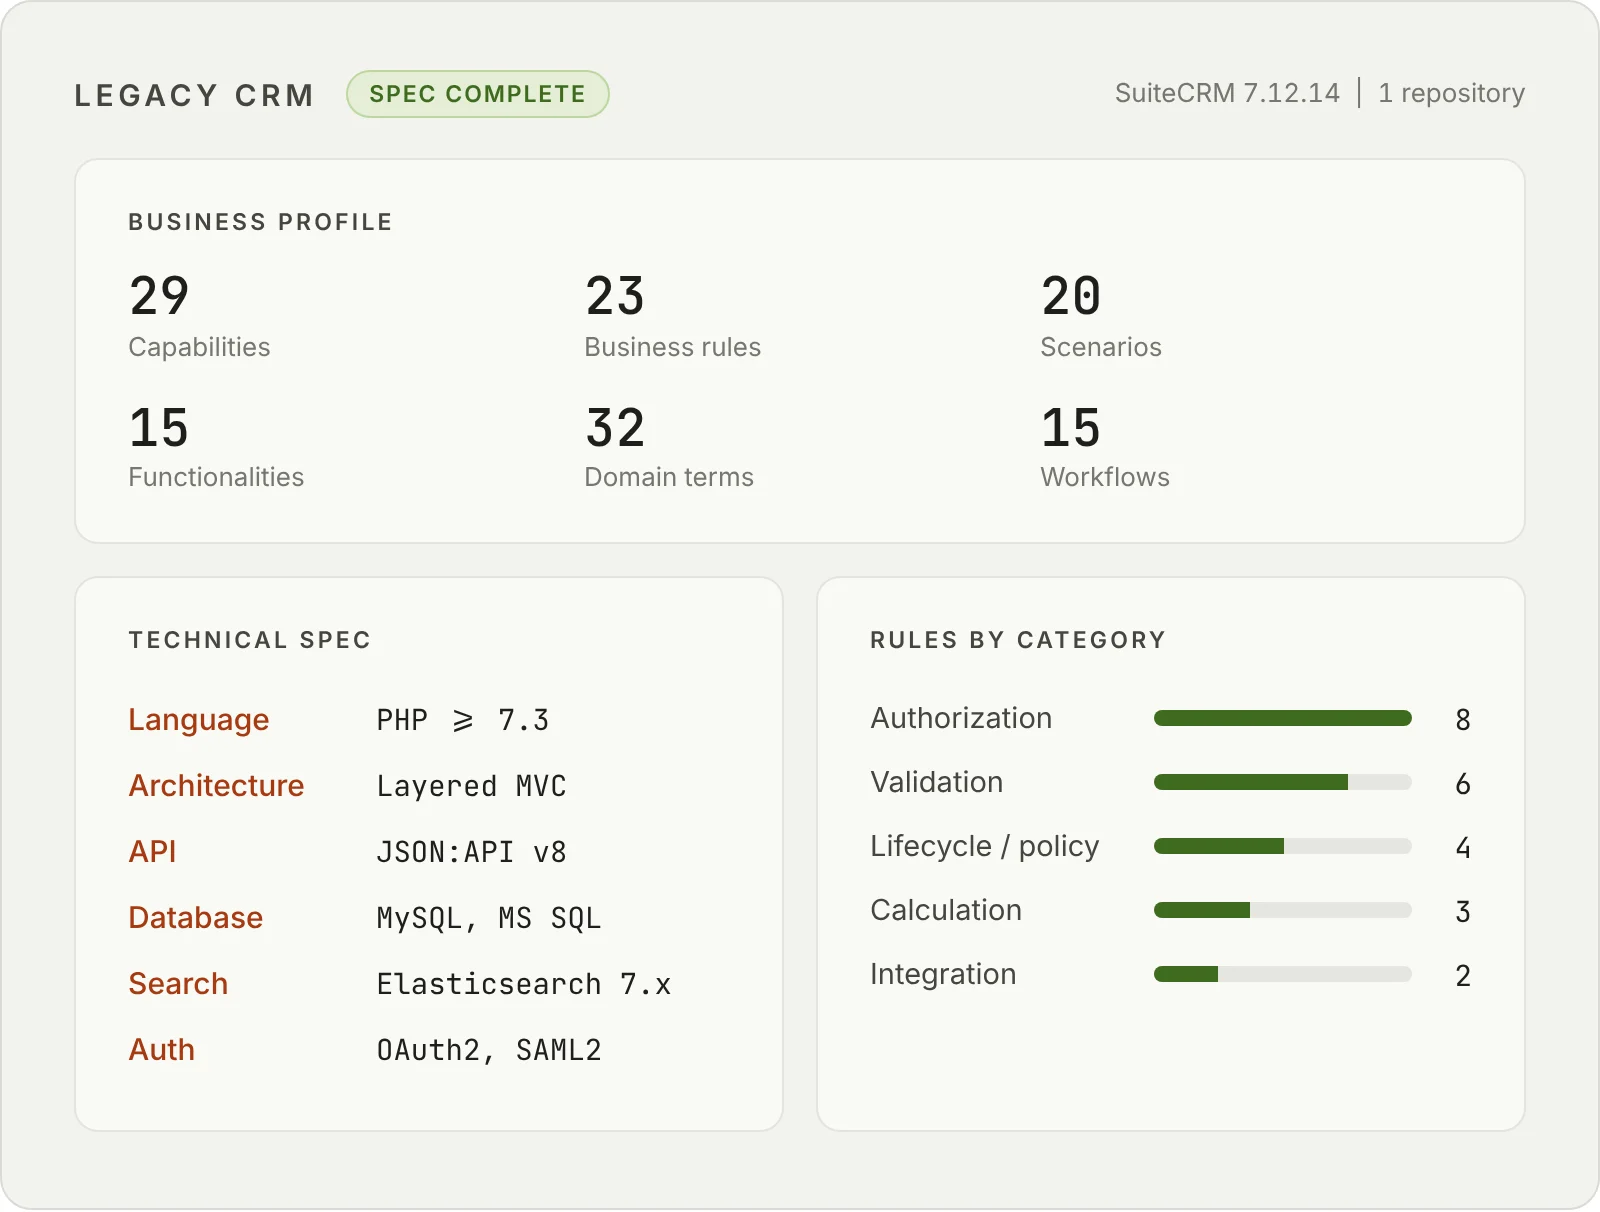
Forge maps business rules, capabilities, and the tech stack directly from the code.
Security Intelligence
Forge runs security checks alongside code analysis from day one. It doesn't rely on AI alone. It combines eight open-source scanners, including Trivy, Grype, Semgrep, Gitleaks, and Checkov, with tools your team already uses, like SonarQube and Snyk. Forge finds known vulnerabilities, outdated packages, and exposed credentials, then explains each risk in plain business terms.
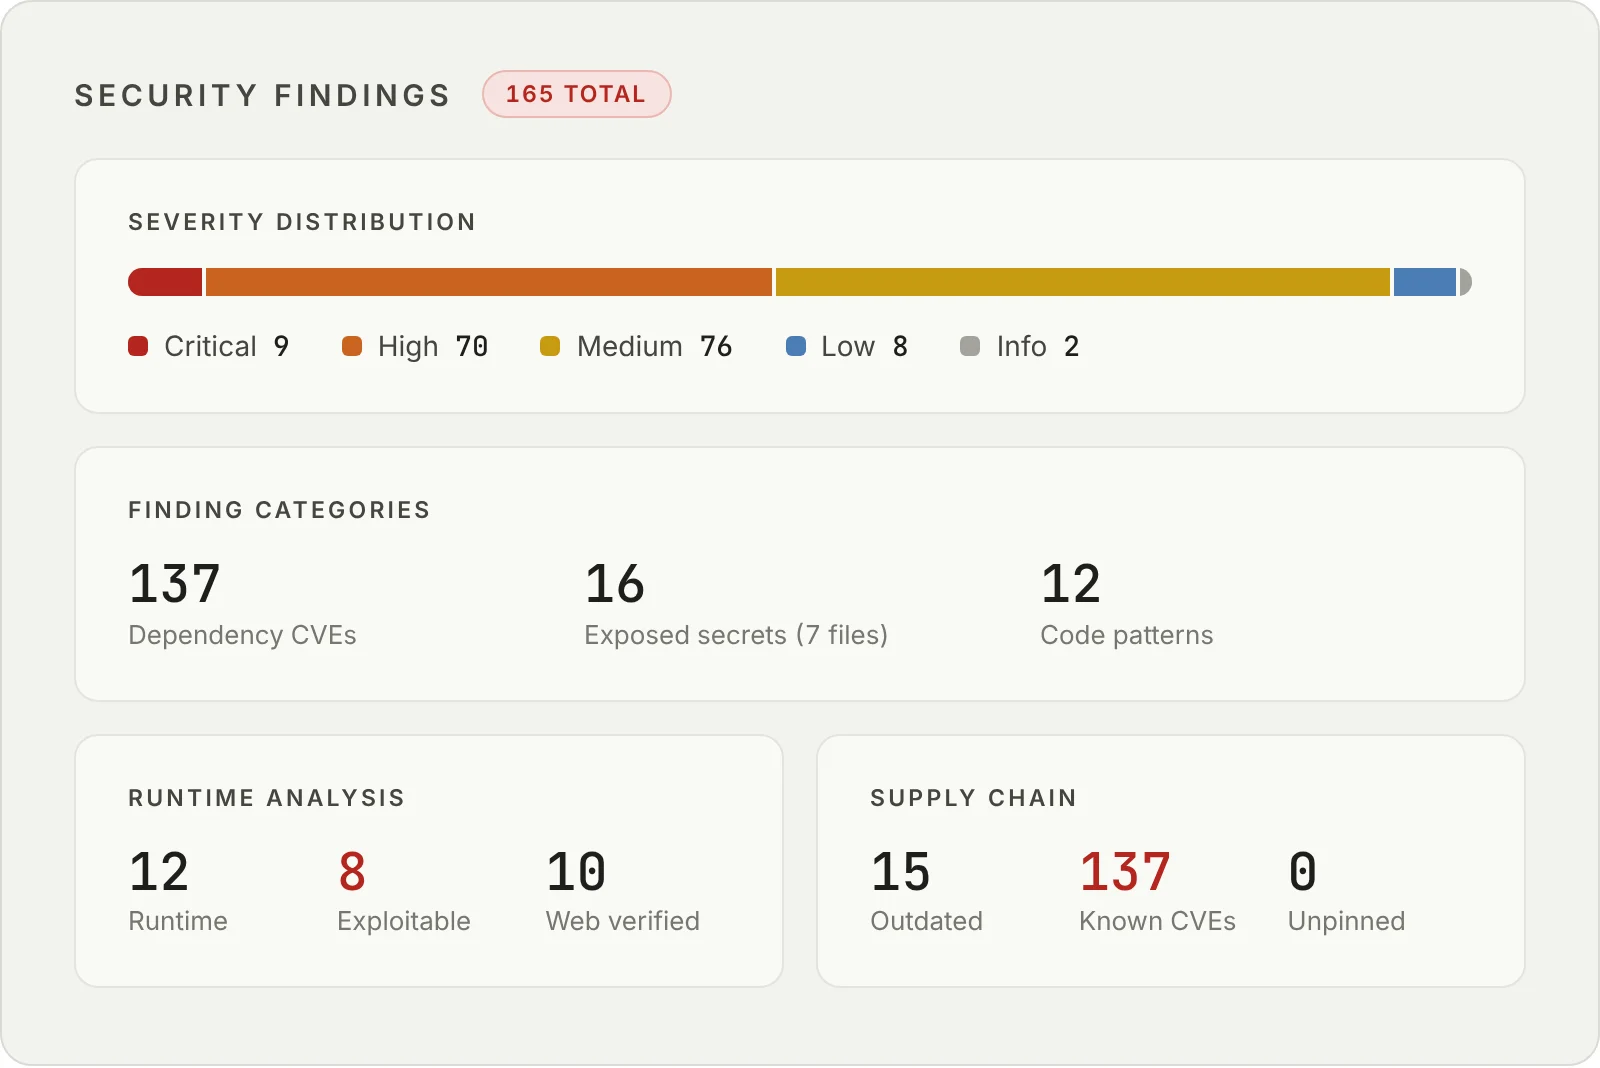
Every finding is grouped by severity, category, runtime impact, and supply chain risk.
When a major threat like PHP2Shell emerges, Forge shows exactly which apps an upgrade will affect. Each rescan tracks what's new, what's fixed, and what's still open. One click on any finding generates a remediation plan, including the PRD updates and work orders needed to fix it.
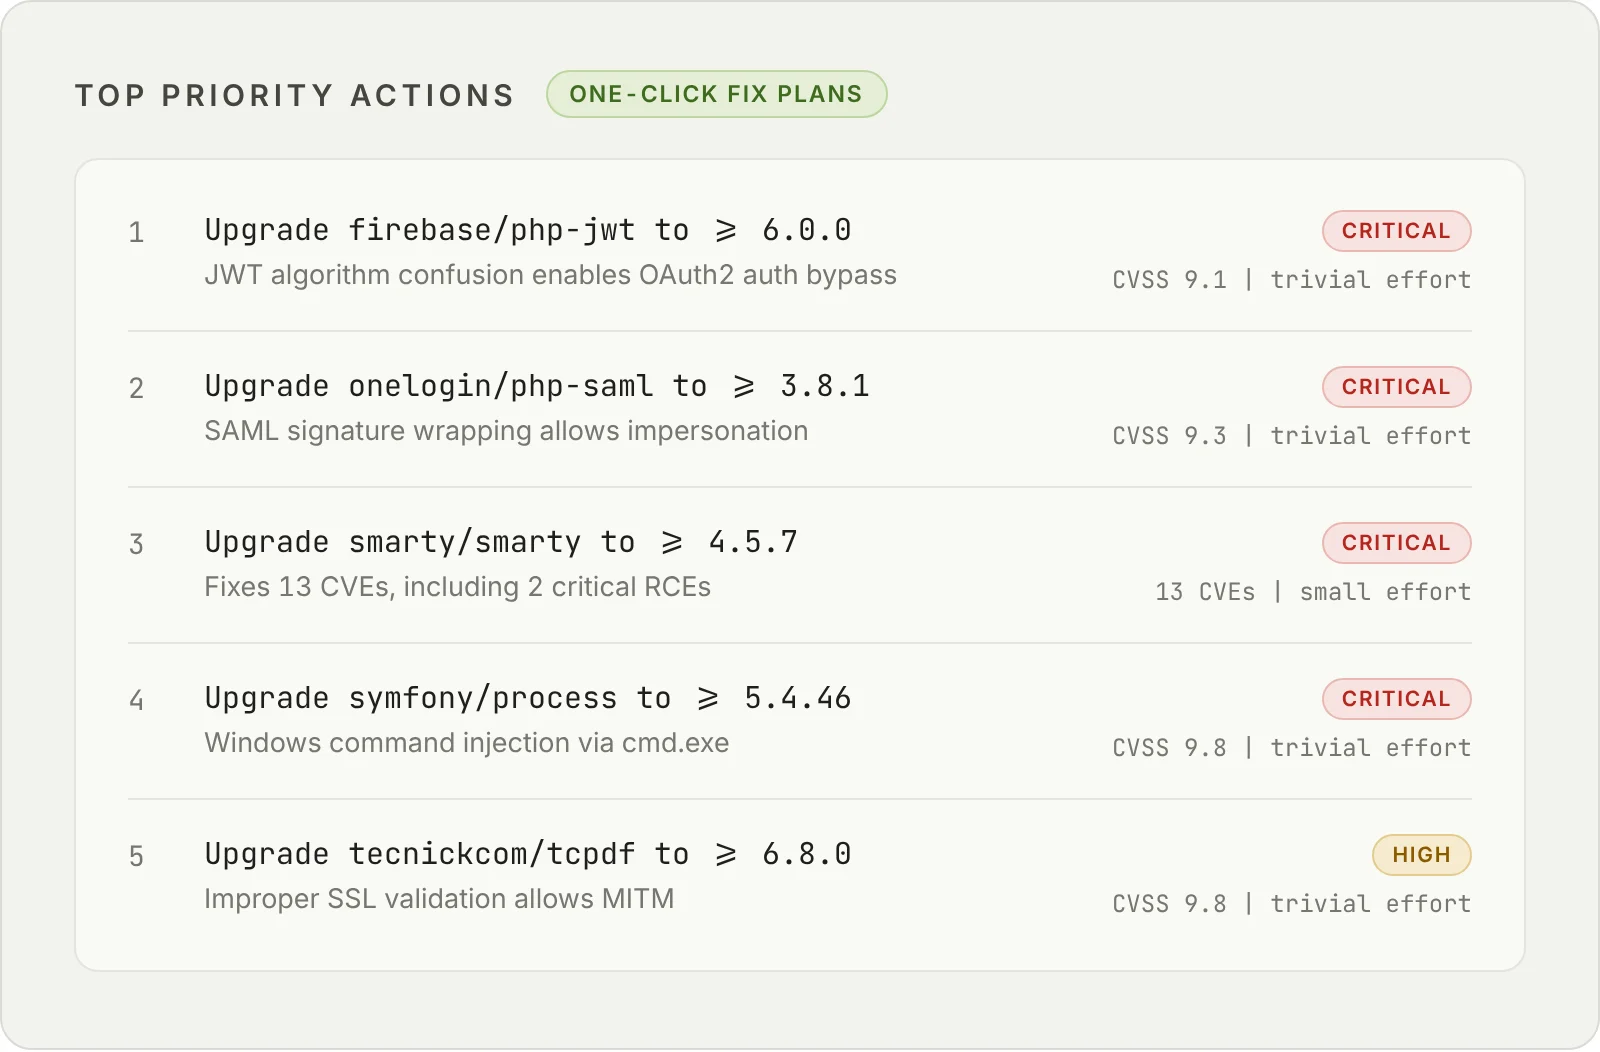
Top priority actions, ranked by risk and effort.
NIST CSF Grading in ForgeScore
ForgeScore, Forge's eight-dimension scorecard, now grades every application from A to F against the NIST Cybersecurity Framework. CISOs and compliance teams get a breakdown of CVEs, exposed secrets, and outdated tech stacks. They also get a branded PDF export with an executive summary for board and audit reporting.
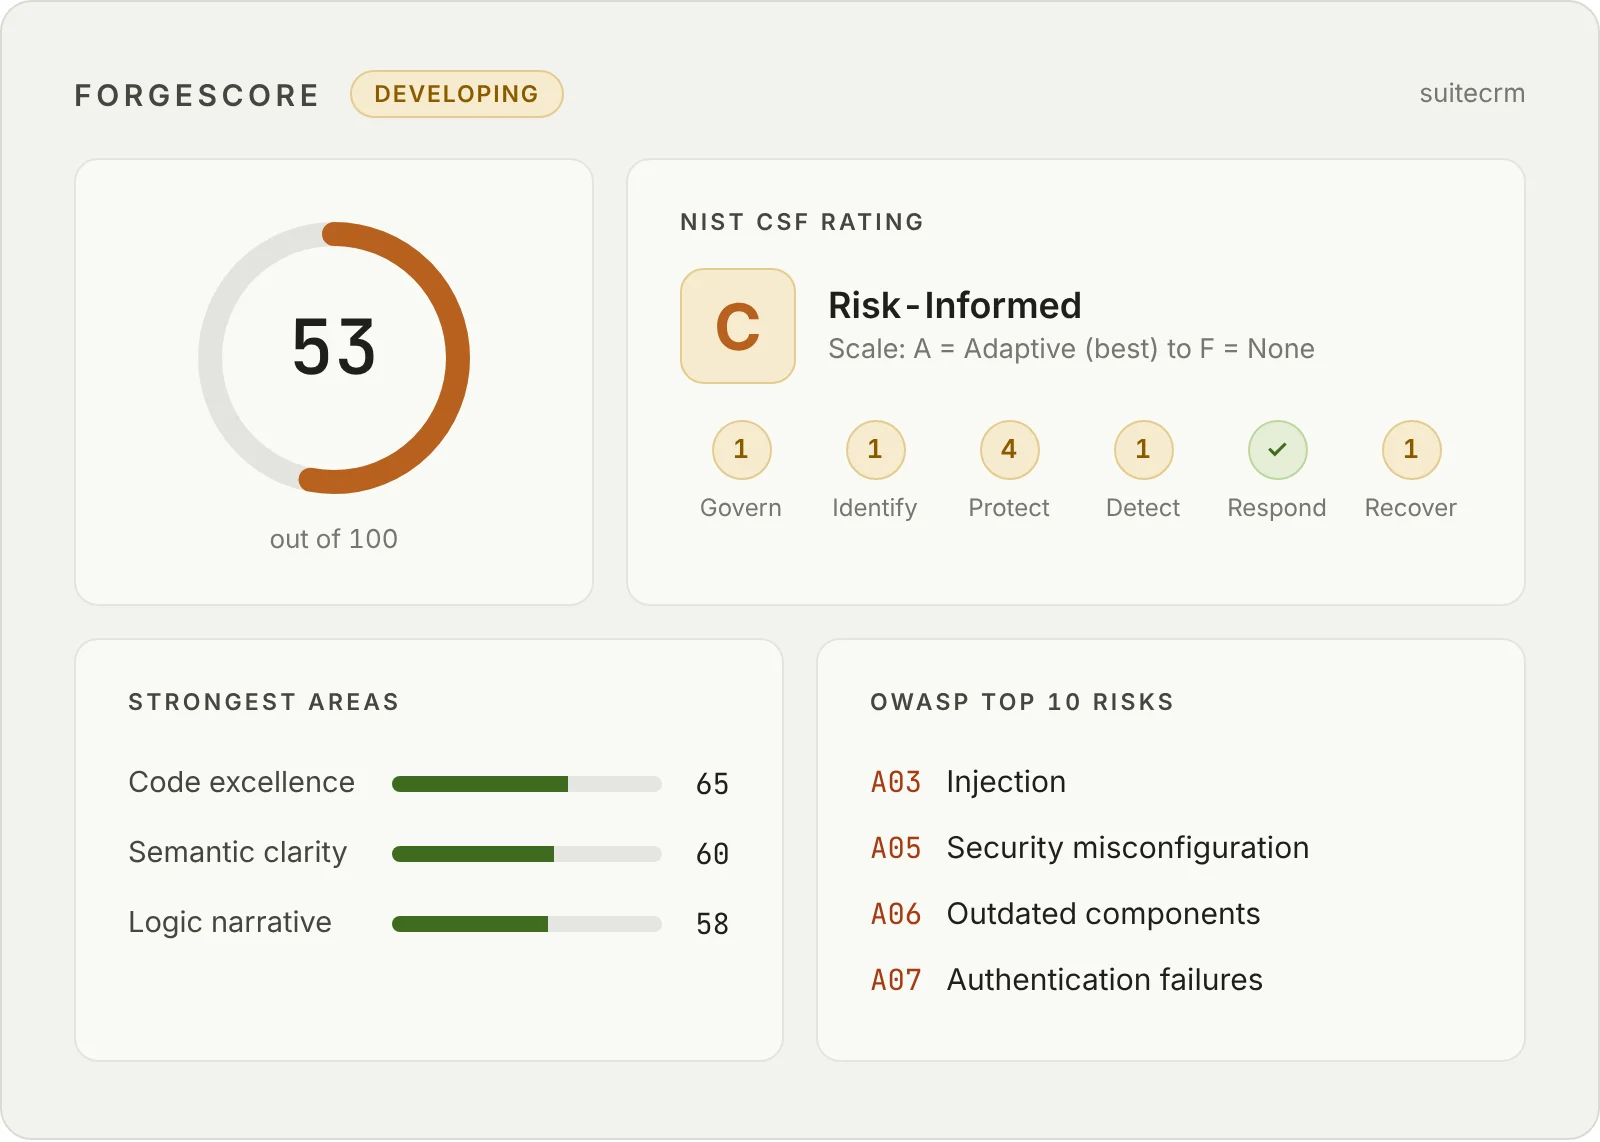
ForgeScore with NIST CSF grading and OWASP Top 10 mapping.
Configurable Pipeline Controls
Admins can add custom approval gates, such as security sign-offs or compliance reviews, at any stage. You can also set the project scope, from a quick bug fix to a full overhaul, and Forge scales the required documentation and story counts to match. Regulated teams get oversight without slowing down simple updates.
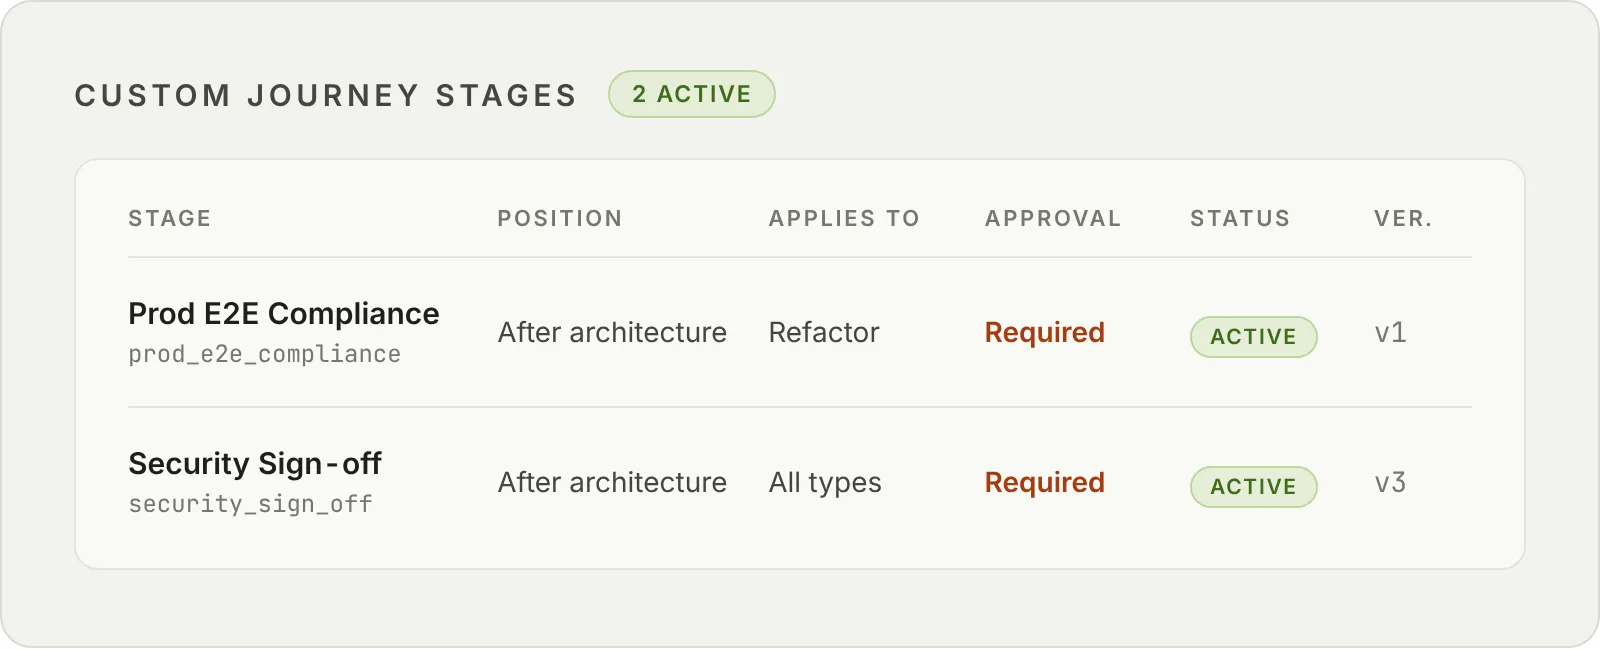
Custom approval stages slot into the modernization pipeline.
Modernize with confidence
AI gives your team speed, and Opsera Forge gives you the guardrails to use it safely. With built-in discovery, plain-English security insights, and NIST compliance reporting, you can modernize legacy apps on solid ground.
Ready to see what is inside your legacy code? Book a walkthrough